

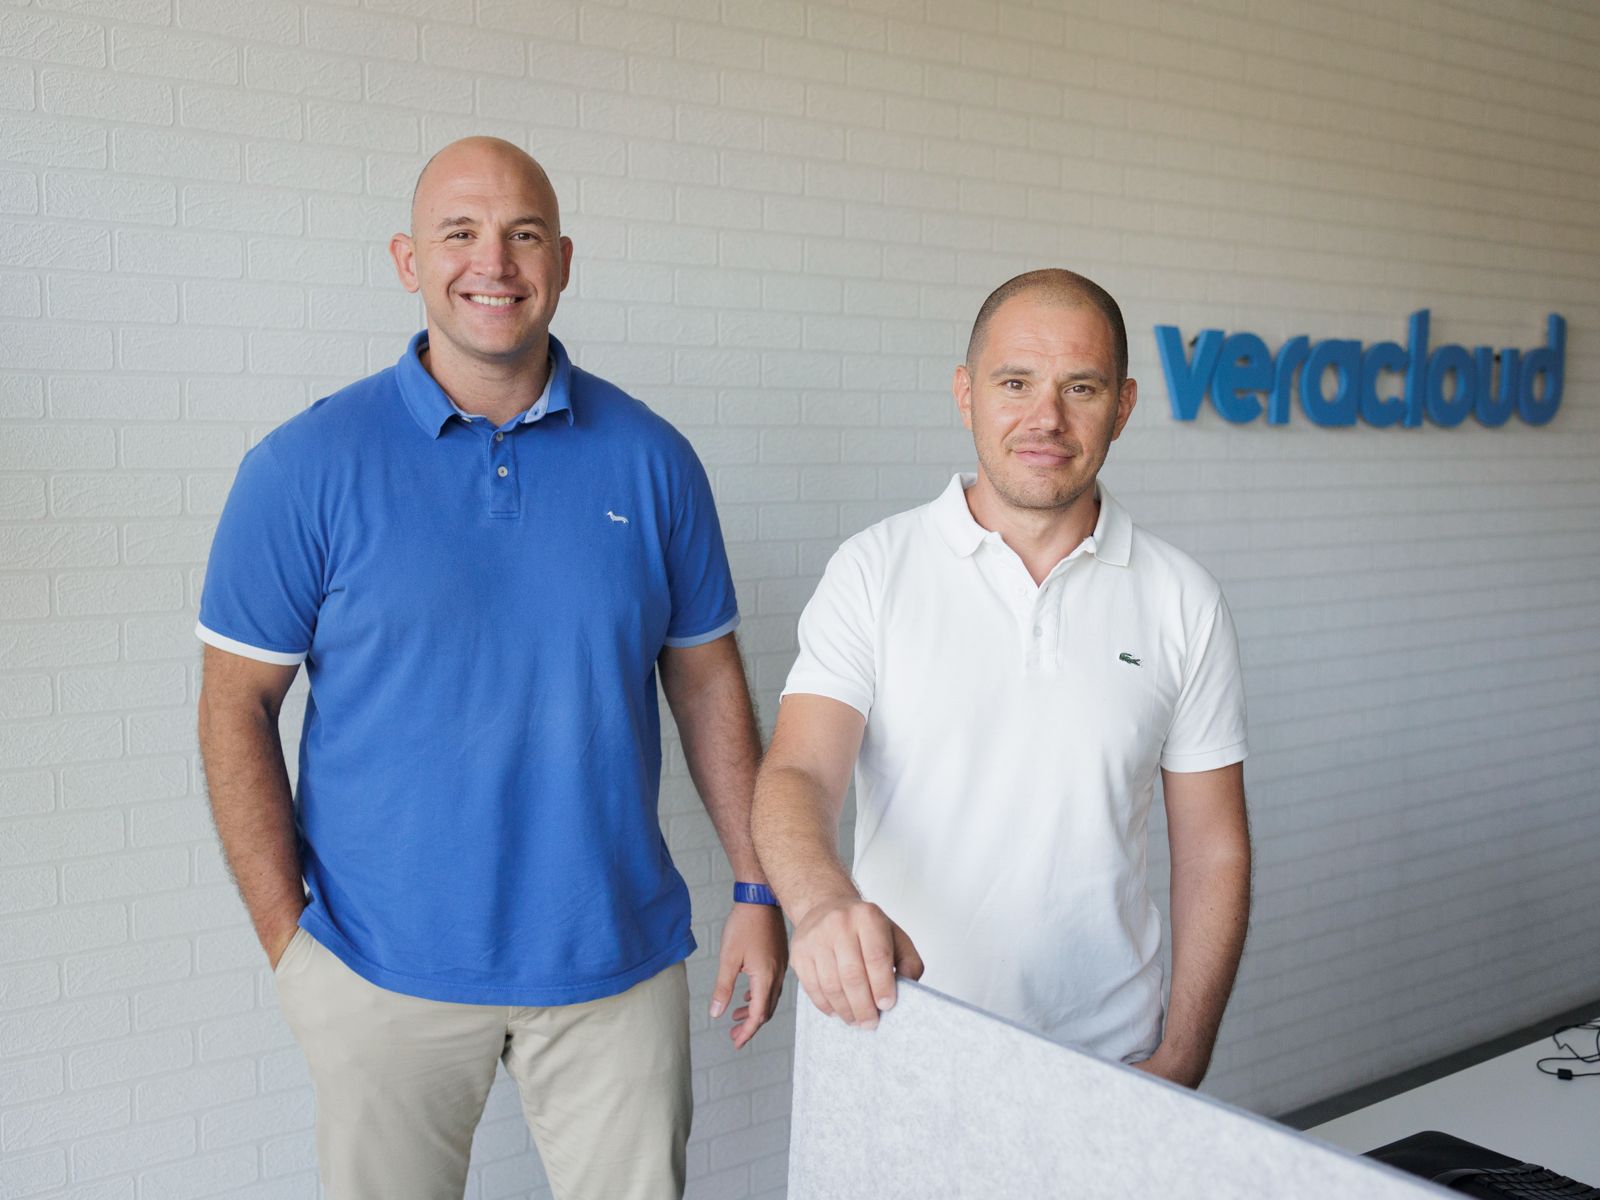
"When a company says they can do it all, it is a bit far-fetched."
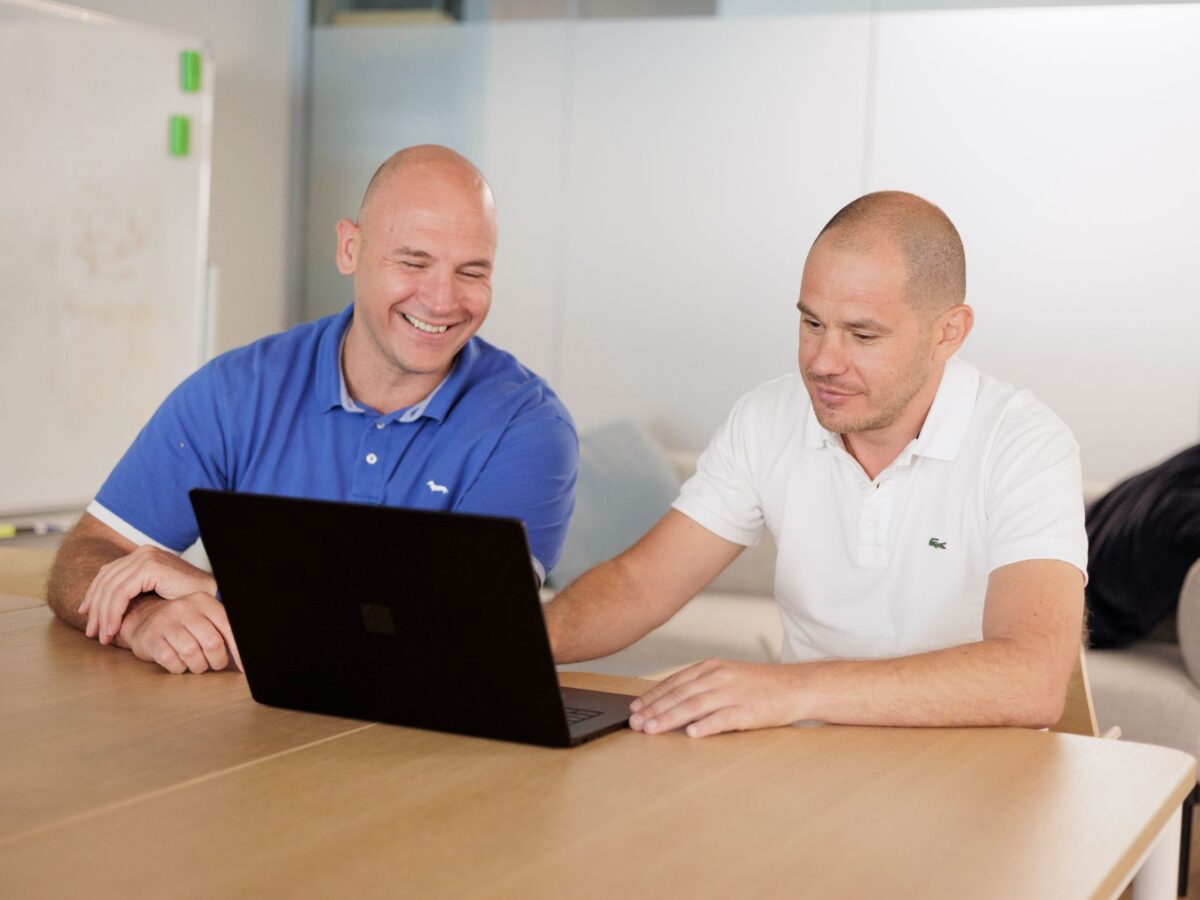
That's how Veracloud co-founder John Ellul answers one of the more persistent myths in the IT industry: that a single provider can realistically cover every layer of a business's cybersecurity.
For Mr Ellul and his co-founder Clint Deguara, cybersecurity stopped being a single discipline a while ago. Cloud security, identity protection, compliance, monitoring, threat detection, incident response: each is its own specialism now, and the list keeps growing as fast as the threats do. Building deep expertise across all of it in-house is expensive, and for most businesses, unrealistic. That's the gap (Managed Service Provider) MSPs and (Managed Security Service Provider) MSSPs exist to fill, and increasingly, no single one of them fills it alone.
Why one provider can't cover everything
"The world of cybersecurity is growing fast, and so are cyber threats," says Mr Ellul. "You can't be a jack of all trades. Outsourcing is becoming necessary, and it's becoming even more crucial to have multiple partners in the field."
Rather than expecting one provider to handle everything, Mr Ellul argues businesses are better served building an ecosystem of specialists, each one deep in a particular area rather than shallow across all of them.
"A partner who has an insight into what they don't offer can create an ecosystem to fill those gaps," he says.
Where does responsibility actually begin and end?
One of the biggest problems businesses run into with technology providers isn't a lack of investment. It's a lack of clarity about who owns what.
"When we speak with clients, a lot of them ask us, 'What are the deliverables you are giving us?'" Mr Ellul says. "But what is not spoken about is what is out of scope."
Security gaps rarely open up because a company failed to spend on protection. More often, they open up because someone assumed another provider already had that piece covered. For Veracloud, defining those boundaries clearly, in writing, isn't a formality. It's the difference between a client actually being protected and a client believing they're protected.
A partner-to-partner approach
Most businesses already work with an IT provider, a cloud platform, maybe a handful of consultants. Veracloud's model is built to slot into that setup rather than replace it.
"All these different partners need to collaborate so that they don't leave any security gaps," says Mr Deguara. "We're here to enhance the current ecosystem and not compete. We avoid finger pointing."
That collaborative approach extends to Veracloud's own vendor relationships. Its partnership with Microsoft, for instance, goes back nearly two decades.
"We have been working with Microsoft for almost 18 years. We've built that relationship," Mr Ellul says.
Mr Deguara sums up where Veracloud sits in that wider ecosystem simply: "We're the security level that connects the dots."
What to actually look for in a cybersecurity partner
So what should a business be screening for when it picks an MSP or MSSP? Mr Deguara starts with specialisation.
"Businesses need a partner with that knowledge and hands-on experience with security, and one that is relevant to what they are doing," he says.
Expertise alone isn't enough, though. Transparency matters just as much, especially as regulatory pressure keeps building.
"The customer should always know what's being monitored, what's being detected and what's being done about it," Mr Deguara explains.
Ownership is the third piece. Veracloud works extensively with regulated clients, where reporting and accountability aren't optional. They're built into frameworks like ISO 27001, DORA and NIS2, all of which leave little room for "we thought someone else was handling that."
"We have logs, reviews and monthly reports. Clients are being serviced," Mr Ellul says.
From insurance policy to strategic pillar
The bigger shift Veracloud is pushing for is a mental one: getting businesses to stop treating cybersecurity like insurance, something bought and then hopefully never needed, and start treating it as part of how the business actually runs.
"We want to be part of your team; a partner and an addition to the IT team," Mr Ellul says. "We want to move away from an insurance policy into a strategic pillar of the company."
That thinking is baked into what Veracloud calls its "secure by design" approach. Building security into infrastructure from day one, instead of retrofitting it once something's already gone wrong. As both co-founders put it, "We want to demystify cloud and security. We need to make it completely business."
Where the next few years get harder
Both co-founders expect the cybersecurity environment to get more complicated before it gets simpler, and AI is a big part of why.
"The risk was always there. AI just speeded things up," Mr Deguara says. "The attack surface area is much bigger now. Everything is on the cloud, so there are more resources to attack."
The numbers back that up. ENISA's 2025 Threat Landscape report attributes the large majority of reported incidents across the EU to ransomware and data breaches, with phishing still the most common way attackers get their first foothold. The same report flags a shift already underway on the other side too. AI is increasingly showing up in attackers' toolkits, not just defenders', automating social engineering and speeding up malware development.
That's making reactive security harder to justify. Businesses can't wait for an incident to respond to it. They need continuous monitoring that catches weaknesses before they're exploited. It also means security has to be built in from the start of any new tool or platform, not bolted on once it's already live, since the same speed that gets a business moving quickly into production also applies to attackers moving quickly into a business's supply chain.
The bottom line
Knowing what you do best, and knowing exactly who to bring in for everything else, might be one of the more underrated cybersecurity strategies a business can adopt.
Businesses looking to map their own gaps can start that conversation with Veracloud directly.
EC President proposes Canada as associate EU member, under-13 social media ban
'I would like to work with you on opening the door for Canada to be the first associate member of ...

‘Our companies have complementary strengths’ – Melita CEO on Epic acquisition
Melita has announced that it is acquiring a 100% stake in Epic.
Ivan Isola launches Riesgo Advisory Limited and takes on Director role
Ivan Isola is a certified public accountant and has been financial consulting for over ten years.
Sarah Stellini joins BetanzaLab as Chief Marketing Officer
The iGaming executive takes on the new role after three years at Neatplay, where she served as Chief Commercial Officer.
